Navigating regulatory complexity:
Building a single compliance architecture
An invitation-only in-person masterclass hosted by ICA & LexisNexis Regulatory Compliance
20 October 2026 | 3PM - 6PM | 6 Park Place, St James's, London SW1A 1LR
Tim Tyler
Vice President
International Compliance Association
Daveena Suri
UK - Content Manager
LexisNexis Regulatory Compliance
James Kent
Head of Legal, Economic Crime
NatWest
Dane Pedro
Head of UK Compliance & MLRO
Mollie
This event has now concluded. You can view all other upcoming ICA events here.
An honest conversation held under the Chatham House Rule
As implementation, supervision and regulatory simplification converge, organisations are no longer managing one wave of regulatory change at a time. DORA, MiCA, the AI Act, the Data Act, cybersecurity requirements, financial-crime reforms and sustainability obligations are progressing at different speeds, but often rely on the same systems, data, suppliers, governance arrangements and operational processes.
For senior compliance leaders, the challenge is therefore not simply to implement each regulation in isolation. It is to understand which requirements apply, how they interact and how they can be translated into controls and evidence that remain effective as the regulatory perimeter continues to evolve.
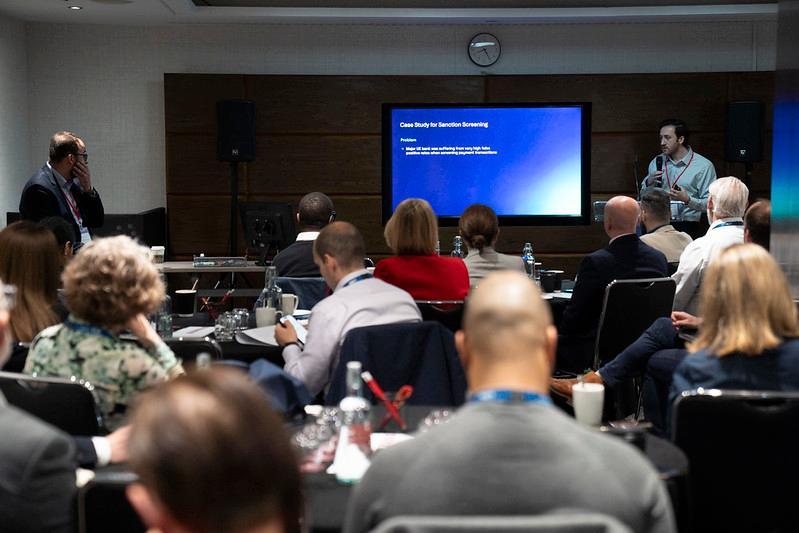
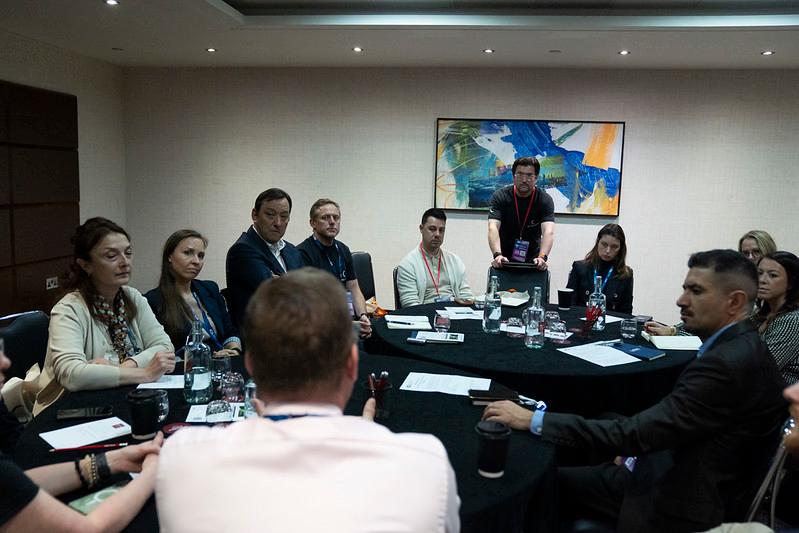
This highly interactive masterclass, held under the Chatham House Rule, will bring together 25–30 senior compliance leaders to examine how organisations can move beyond regulation-by-regulation programmes and develop a more coherent, capability-led compliance operating model.
Through practical examples, facilitated peer discussion and real-world implementation experience, attendees will explore how common capabilities including regulatory change management, data governance, third-party risk, incident management, monitoring, testing and evidence management can support multiple regulatory regimes while preserving their distinct scope, thresholds and reporting requirements.
The discussion will also consider how organisations can strengthen traceability from legal source and applicability decision through to ownership, control operation, evidence, assurance and remediation helping them demonstrate not only that requirements have been implemented, but that they are working effectively in practice.
Attendees will leave with:
- A practical framework for mapping the status, applicability and interaction of major EU regulatory requirements
- A clearer understanding of where controls, processes and evidence can be shared and where regulatory distinctions must be preserved
- Approaches to strengthening traceability from legal obligation to operating evidence
- Practical ideas for reducing duplication, identifying control gaps and improving regulatory change readiness
- A clearer view of what a sustainable, adaptable and supervision-ready compliance operating model looks like
Who should attend?
This session is designed for senior risk and compliance professionals, including:
- CCOs
- CROs
- Director / Head of Compliance
- Director / Head of Regulatory Compliance
- General Counsel
- Director / Head of Risk & Compliance
- Director / Head of Financial Crime Compliance
Agenda at a glance
- 14:30: Registration and arrival
- 15:00: Opening remarks, context and intelligence, followed by a practitioner panel
- 16:00: Interactive group discussions and benchmarking
- 17:00: Networking drinks reception
- 18:00: Event close